Security Operation Center Architecture
Security Operation Center Architecture is the structured design of people, processes and technology that lets an organisation monitor, detect and respond to cyber threats continuously. It combines log sources, a SIEM for correlation, SOAR for automation and EDR for endpoint visibility. SOC analysts work inside this architecture to triage security alerts, investigate incidents and drive incident response to closure.
Table of Contents
Introduction
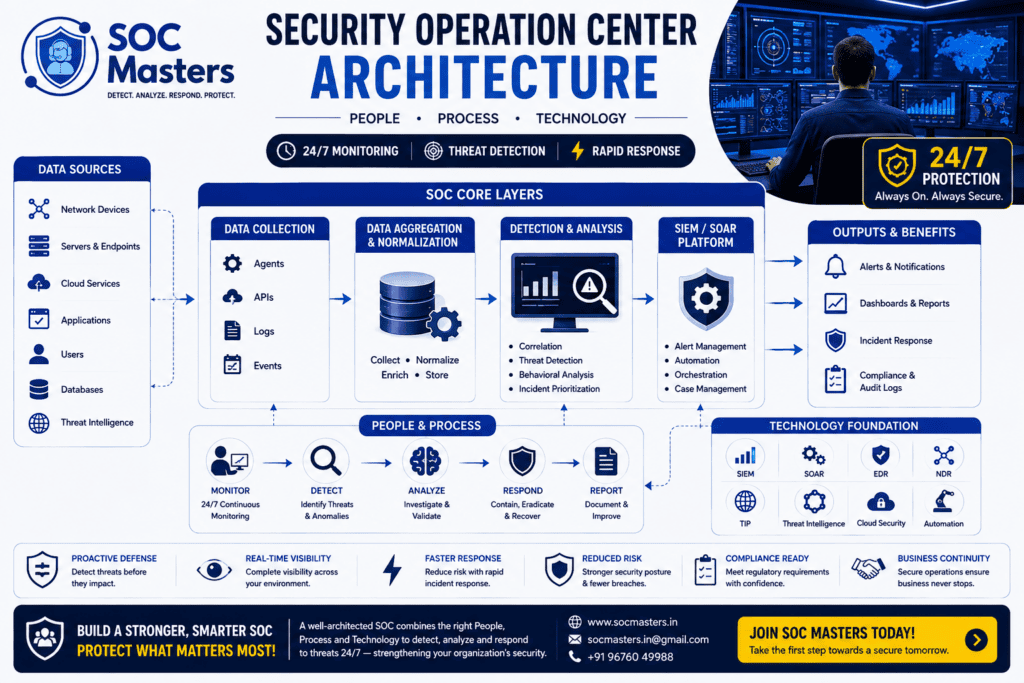
A Security Operations Center is the team and technology stack an organisation uses to watch its network, endpoints, identities and cloud workloads for signs of attack. Security Operation Center Architecture is the blueprint behind it: how logs are collected, where they are normalised, which platform correlates them, who sees the alert first, and how an incident moves from detection to containment to closure.
Without it, a SOC is just dashboards — alerts with no owner and real intrusions unnoticed in the queue. With a defined SOC architecture, every log has a destination, every alert has a route, and every analyst knows where their responsibility ends.
That is why architecture is the first serious topic in any credible SOC Analyst Training in Hyderabad programme. If the term itself is new to you, start with what a SOC actually is. Tools change every quarter; architecture transfers between employers.
What Is Security Operation Center Architecture?
Security Operations Center Architecture arranges SOC infrastructure, people, processes and technology into one operating model for security monitoring, threat detection and incident response. It works as four stacked layers:
Data layer. Servers, endpoints, firewalls, identity providers and cloud platforms generate logs and telemetry.
Collection and normalisation layer. Agents, forwarders and APIs move raw data into a central platform, where it is parsed into a consistent schema so a Windows logon and an AWS API call can be compared directly.
Detection and analytics layer. Correlation rules, behavioural analytics and threat intelligence turn normalised events into alerts worth human attention.
Response layer. Analysts, playbooks, ticketing and containment convert alerts into decisions, and decisions into action.
People, processes and technology run through all four. Remove one and it breaks: tools without process produce noise, process without people produces backlog, people without tools produce guesswork.
Why Is SOC Architecture Important?
- 24/7 security monitoring. Shift coverage with documented handover is an architectural decision, not an afterthought.
- Early threat detection. Centralised log management correlates a failed logon in one system and a privilege change in another into one story.
- Faster incident response. Defined escalation paths remove the “who owns this?” delay that costs hours.
- Centralised visibility. One console instead of twelve reduces blind spots between products.
- Reduced response time. Automation handles enrichment so analysts spend time on decisions.
- Compliance and reporting. ISO 27001, PCI DSS and India’s CERT-In directions all expect demonstrable log retention, monitoring and incident handling.
- Stronger security posture. Every closed incident feeds a detection improvement — possible only with a feedback loop.
Key Components of a Security Operations Center
People
Role | Core responsibility |
SOC Manager | Staffing, shift coverage, metrics, escalation |
SOC L1 Analyst | Alert monitoring, triage, ticket creation |
SOC L2 Analyst | Investigation, correlation analysis, incident scoping |
SOC L3 Analyst | Complex threats, malware analysis, threat hunting |
Threat Hunter | Hypothesis-driven searches for undetected activity |
Incident Responder | Containment, eradication, recovery, forensics |
Security Engineer | Log onboarding, rule tuning, platform health |
Processes
Alert monitoring, alert triage, incident investigation, incident response, threat hunting, threat intelligence and reporting — each with a written runbook. The difference between an average SOC and a strong one is usually process maturity, not tool budget.
Technology
SIEM, SOAR, EDR, firewalls, IDS/IPS, vulnerability management, threat intelligence platforms and network security monitoring — the SOC monitoring tools that generate, enrich and act on telemetry.
Security Operation Center Architecture Diagram and Workflow
The standard SOC workflow follows one path:
Data Sources → Log Collection → SIEM → Alert Detection → SOC Analyst → Investigation → Incident Response → Remediation → Reporting
Data sources. Servers write authentication and process logs, endpoints send EDR telemetry, firewalls record allowed and denied traffic, and cloud platforms produce activity logs such as Azure sign-in logs and AWS CloudTrail.
Log collection. Forwarders, agents and API connectors ship this data centrally. Bandwidth, retention cost and time normalisation are decided here — expensive to fix later.
SIEM. The platform parses each log into a common schema, then correlates across sources. One failed login is noise; forty failed logins followed by a success from an unusual location is a detection.
Alert detection. Correlation rules, anomaly models and threat intelligence matches raise alerts with a severity score.
SOC analyst. An L1 analyst checks context and decides: false positive, benign true positive, or escalate.
Investigation and response. L2 and L3 analysts pull supporting logs, build a timeline, confirm scope and hand containment to the response team.
Remediation and reporting. Root cause is fixed, detection gaps closed, the incident documented for audit.
Types of SOC Architecture
Organisations choose between several SOC deployment models depending on scale, budget and regulation.
Centralised SOC. One team, one location, one platform. Simplest to govern and common in mid-sized Indian enterprises, but a single point of failure.
Distributed SOC. Regional SOCs sharing detection content and escalation standards. Suits multinationals with data-residency obligations; needs strict governance.
Virtual SOC. No dedicated facility; analysts work remotely on a cloud-hosted platform. Cost-effective for smaller organisations, but demands tighter access control.
Cloud-based SOC. Built on a cloud-native SIEM with no on-premises collection beyond forwarders. Scales fast and shifts cost from capital to consumption, so ingestion volume must be managed.
Hybrid SOC. An internal team handles business-context-heavy work while an MSSP covers nights and weekends — now the dominant pattern among Indian GCCs and BFSI operations, and the environment most freshers join. Each of these is compared in detail in our guide to different types of security operations centers.
SOC Security Monitoring Architecture
Continuous monitoring is a loop, not a queue. Logs are collected from every in-scope source and correlated across sources and time windows. Real-time rules fire on known-bad patterns while scheduled analytics catch slower behaviour such as low-and-slow data staging. Alerts arrive with severity and enrichment attached, and anything above the triage threshold is escalated with a documented handover.
Mature SOCs measure this loop: log source availability, mean time to detect and respond, false positive rate per rule. A rule producing ninety false positives a week is an architecture problem, not an analyst problem.
Role of SIEM in SOC Architecture
The SIEM is the centre of gravity in most SOC architectures. It collects logs from every onboarded source, normalises them into a common schema, correlates events, generates alerts, and supports dashboards, investigation and compliance reporting — a layout covered in SIEM architecture.
Commonly deployed platforms include Microsoft Sentinel, Splunk, IBM QRadar and Google Security Operations (formerly Chronicle). Three 2026 realities are worth knowing before an interview:
- Microsoft Sentinel now runs primarily through the Microsoft Defender portal. Sentinel in the Azure portal will be retired on 31 March 2027 — extended from the original 1 July 2026 deadline — so new deployments are designed around the unified Defender experience from day one.
- IBM QRadar needs a careful answer. IBM divested its QRadar SaaS assets to Palo Alto Networks in September 2024, and that SaaS line reached end of life on 14 April 2026, with QRadar EDR and XDR following on 31 August 2026. On-premises QRadar SIEM was not part of the divestiture and continues on its own release track — “QRadar is dead” is inaccurate.
- Google Security Operations combines SIEM and SOAR in one platform, normalising everything into its Unified Data Model.
This is why SIEM depth matters in SOC Analyst Training in Hyderabad. Employers hiring in HITEC City, Gachibowli and the Financial District test whether you can write a query, read a correlation rule and explain why an alert fired — not whether you can recite a definition. The layer-by-layer view of how a SIEM is put together is covered in our SIEM architecture guide.
Role of SOAR in SOC Architecture
Security Orchestration, Automation and Response sits between the SIEM and the analyst. When an alert fires, a playbook enriches it automatically: source IP reputation, the user’s authentication history, file hash lookups, asset owner, and ticket creation — all before a human opens it. For higher-confidence detections it can act directly: disable an account, isolate an endpoint, block a domain, or quarantine an email across every mailbox that received it.
The practical impact of security automation is analyst capacity. Enrichment that took ten minutes now happens in seconds, so L1 analysts spend their shift on judgement calls rather than copy-paste work.
Role of EDR in SOC Architecture
Endpoint Detection and Response provides depth network logs cannot. EDR agents record process creation, command-line arguments, parent-child relationships, registry modifications, file writes and outbound connections on every managed device.
That telemetry supports suspicious process detection, malware identification, behavioural analysis, investigation with a full process tree, and containment through host isolation. When a SIEM alert says “unusual PowerShell activity on a finance workstation,” EDR tells the analyst which parent process spawned it and what the command line contained.
SOC Analyst Roles and Responsibilities
The tiering below is the standard structure; our full breakdown of analyst duties at each tier expands on it.
SOC L1 Analyst. Monitors the alert queue, performs initial triage, identifies false positives, creates tickets and escalates per the runbook. The typical entry point for freshers, where disciplined triage under pressure matters most.
SOC L2 Analyst. Handles escalated alerts, investigates across multiple log sources, runs correlation analysis and joins threat hunts. Usually reached after 18 months to three years of L1 work.
SOC L3 Analyst. Investigates complex threats, performs malware analysis, leads advanced threat hunting and works with security engineering — authoring detection content rather than consuming it.
SOC Architecture Tools
The main technologies and tools used in a SOC, grouped by function:
Tool Category | Examples | Primary Purpose |
SIEM | Microsoft Sentinel, Splunk, Google SecOps, QRadar | Centralised security monitoring and correlation |
SOAR | Playbook and orchestration platforms | Incident automation and enrichment |
EDR / XDR | Endpoint security platforms | Endpoint detection and containment |
IDS / IPS | Network security appliances | Network threat detection and blocking |
Firewall | Enterprise and cloud firewalls | Traffic filtering and segmentation |
Threat Intelligence | TI platforms and feeds | Context on indicators and threat actors |
Vulnerability Management | Scanning platforms | Vulnerability identification and prioritisation |
Log Management | Collectors, forwarders, data lakes | Log retention and long-term search |
SOC Architecture and Incident Response
The incident response process — aligned with <a href=”https://csrc.nist.gov/pubs/sp/800/61/r3/final” target=”_blank” rel=”noopener”>NIST SP 800-61 Rev. 3</a> — maps directly onto SOC architecture:
- Preparation — runbooks written, log sources onboarded, escalation contacts agreed.
- Detection — the SIEM or EDR raises the alert; L1 confirms it is real.
- Analysis — L2 builds the timeline and determines scope, impact and affected accounts.
- Containment — accounts disabled, hosts isolated, indicators blocked.
- Eradication — malicious artefacts removed, persistence cleared, credentials rotated.
- Recovery — systems restored and monitored closely for recurrence.
- Lessons learned — root cause documented, detection gaps closed, runbooks updated.
Step seven decides whether the SOC improves. Every incident should produce one artefact: a new detection rule, a tuned threshold, or a corrected runbook.
SOC Architecture and Threat Intelligence
Threat intelligence gives raw alerts meaning. Indicators of compromise — IP addresses, domains, URLs and file hashes — are matched against incoming telemetry so analysts know whether an artefact has appeared in known campaigns. Above indicators sits knowledge of threat actors and their tactics and techniques.
The <a href=”https://attack.mitre.org/matrices/enterprise/” target=”_blank” rel=”noopener”>MITRE ATT&CK Enterprise Matrix</a> is the common language for this: analysts map an alert to a technique, then ask what comes next in the attack chain. Two 2026 updates matter. Version 18 replaced the old Detections and Data Sources model with Detection Strategies and Analytics, and version 19 — released 28 April 2026 — split Defense Evasion into two tactics, Stealth and Defense Impairment. Enterprise ATT&CK now spans 15 tactics and 222 techniques; material still teaching 14 tactics is out of date.
SOC Dashboard and Monitoring
A useful SOC dashboard answers “what needs attention right now?” in ten seconds: open security alerts by severity and age, critical incidents in progress, failed authentication spikes, malware and EDR detections, suspicious outbound traffic, threat intelligence matches, log source health and incident status by owner. Dashboards showing only totals are decoration; those showing ageing, ownership and log source gaps drive action.
SOC Workflow Example
Suspicious login → SIEM alert → L1 triage → log investigation → L2 escalation → threat intelligence check → account containment → incident documentation
A finance user’s account authenticates from an unfamiliar country twenty minutes after a normal Hyderabad login, and the SIEM’s impossible-travel rule fires a medium-severity alert.
The L1 analyst confirms there is no approved travel, checks whether multi-factor authentication was satisfied, and finds the second login came from a residential proxy range — enough to escalate.
The L2 analyst pulls authentication history, mailbox audit logs and EDR telemetry. A forwarding rule was created four minutes after the login — a classic business email compromise pattern — and threat intelligence places the source IP in credential-phishing infrastructure.
Containment follows: session revoked, password reset, forwarding rule removed, mailbox checked for exfiltration. The incident is documented with a full timeline, and a new detection rule proposed for forwarding rules created soon after an anomalous login. That one alert touched log management, alert triage, threat intelligence, incident response and reporting — the whole architecture, in a single shift.
Skills Required to Work in a SOC
Technical skills. Networking fundamentals (TCP/IP, DNS, HTTP, proxies), Linux and Windows logging, SIEM query languages, log analysis, threat detection, incident response, MITRE ATT&CK and threat intelligence.
Soft skills. Clear written communication, analytical thinking, attention to detail, disciplined documentation and cross-shift collaboration. An investigation documented badly is worth little to the next shift. A step-by-step learning path should sequence these skills for beginners.
Why SOC Architecture Knowledge Matters for SOC Analysts
Architecture knowledge changes how an analyst works. It shows where an alert originated and which log source answers the next question, so nobody searches blindly. It lets an analyst recognise an attack path across identity, endpoint and network instead of treating each alert as isolated, and it clarifies who owns the next action.
This is why serious SOC Analyst Training in Hyderabad starts with architecture before tools. Candidates who can explain how a log travels from an endpoint to an analyst’s screen interview very differently from those who can only name products.
How SOC Analyst Training in Hyderabad Can Help Beginners
A SOC Analyst course in Hyderabad worth your time and money covers architecture end to end, hands-on SIEM work, real log analysis rather than screenshots, alert triage practice, the incident response lifecycle, threat intelligence, EDR investigation, SOAR playbooks and realistic projects — the structure followed at SOC Masters.
Ask specific questions before enrolling. Which SIEM will I use, for how many hours? Are labs live or recorded? Which certification does the syllabus map to? Who is teaching, and what did they do in a SOC? Treat any promise of assured hiring outcomes with caution — results depend on your preparation, the employer and the market.
For a Microsoft-aligned path, the <a href=”https://learn.microsoft.com/en-us/credentials/certifications/security-operations-analyst/” target=”_blank” rel=”noopener”>Microsoft Certified: Security Operations Analyst Associate (SC-200)</a> is the most relevant credential. Its syllabus was restructured on 16 April 2026 into three domains — “manage a security operations environment” now carries 40–45% weight — with a minor update on 28 July 2026, so check you are studying the current outline.
Career Opportunities After SOC Analyst Training
Roles include SOC Analyst L1, L2 and L3, Security Operations Analyst, Cybersecurity Analyst, Incident Response Analyst, Threat Intelligence Analyst and Security Monitoring Analyst. Working through realistic SOC analyst interview questions is the fastest way to find gaps.
A cybersecurity career in Hyderabad has a specific shape. The city’s global capability centres — weighted toward BFSI, healthcare, pharmaceuticals and technology — run security operations for global parents, meaning round-the-clock shifts and early exposure to enterprise-scale tooling. GCCs took roughly half of Hyderabad’s office space absorption in 2025, and cybersecurity is among the most actively hired functions within them.
Compensation varies by employer, shift pattern and experience. As a market estimate only, entry-level L1 roles in Hyderabad commonly fall in the ₹3.5–6 LPA range, L2 roles ₹8–14 LPA, and L3 or specialist roles above that. These are indicative market estimates compiled from publicly available job listings and industry reporting — not commitments. Actual offers depend on the employer, your interview performance and market conditions.
SOC Architecture vs Traditional Security Monitoring
Feature | Traditional Monitoring | Modern SOC Architecture |
Monitoring | Limited, business hours | Continuous, 24/7 |
Data collection | Siloed per product | Centralised and normalised |
Detection | Manual review | Automated plus analyst driven |
Response | Reactive | Structured and documented |
Threat intelligence | Limited or absent | Integrated into detection |
Automation | Low | SOAR enabled |
Improvement | Ad hoc | Feedback loop from every incident |
Future of Security Operations Center Architecture
Four shifts are already visible in production environments.
AI-assisted operations. Assistants embedded in SIEM platforms summarise incidents, translate plain English into query syntax and suggest next steps. They compress the time between alert and understanding — they do not remove accountability.
Consolidation into unified platforms. Vendors are collapsing SIEM, SOAR and XDR into single consoles; Sentinel’s move into the Defender portal is the clearest example. Less context-switching, more risk in one platform decision.
Cloud-native, data-tiered SOCs. Retention is splitting into hot analytics tiers and cheaper long-term tiers, making data architecture a real design skill.
Automated investigation. Correlation engines increasingly group related alerts into single incidents before a human sees them, changing what L1 work looks like. The direction is clear: less manual enrichment, more detection engineering, threat hunting and validation. Entry-level roles are not disappearing, but the bar is moving toward analysts who can judge whether the automation got it right.
Key Takeaways
- Security Operation Center Architecture combines people, processes and technology into one model for continuous security monitoring.
- The SIEM is the architectural centre — collecting, normalising, correlating and alerting — while SOAR automates response and EDR supplies endpoint depth.
- SOC analysts work in tiers: L1 triages, L2 investigates, L3 handles complex threats and builds detection content.
- Incident response is a seven-stage lifecycle; lessons learned is the stage that turns incidents into better detection.
- Threat intelligence and MITRE ATT&CK give analysts the context to interpret alerts rather than just close them.
- Platform facts move fast — Sentinel’s Azure portal retirement, QRadar’s SaaS end-of-life and the ATT&CK v19 tactic split all changed this past year.
- Architecture knowledge, not tool memorisation, makes a SOC analyst employable across environments.
Conclusion
Security Operation Center Architecture separates a functioning security operation from a pile of alerts nobody owns. People supply judgement, processes supply consistency, technology supplies scale. SIEM correlates, SOAR automates, EDR sees the endpoint, threat intelligence supplies meaning.
If you are evaluating SOC Analyst Training in Hyderabad, judge it by how much time it spends on architecture, live log analysis and real triage practice — that is what carries into your first shift.
Start by learning how the pieces connect: where a log begins, how it becomes an alert, and what happens after you escalate it. Our cyber security course in Hyderabad covers that foundation.
Frequently Asked Questions
1. What is Security Operation Center Architecture?
It is the structured design of people, processes and technology used to monitor, detect, investigate and respond to threats — defining how logs flow from data sources through a SIEM to analysts, and how alerts become incidents.
2. What are the main components of SOC architecture?
Three pillars: people (L1, L2 and L3 analysts, threat hunters, incident responders, engineers), processes (monitoring, triage, investigation, response, reporting) and technology (SIEM, SOAR, EDR, firewalls, IDS/IPS and threat intelligence).
3. How does a SOC work?
Data sources send logs to a central platform. The SIEM normalises and correlates them, then raises alerts. An L1 analyst triages each alert and escalates real threats to L2 or L3. Confirmed incidents move through containment, eradication and recovery.
4. What tools are used in a SOC?
SIEM platforms such as Microsoft Sentinel, Splunk, Google Security Operations and QRadar; SOAR for automation; EDR for endpoint telemetry; firewalls and IDS/IPS for network control; plus threat intelligence and vulnerability management.
5. What is the role of SIEM in SOC architecture?
The SIEM collects logs from every source, normalises them into a common schema, correlates events, applies detection rules, generates alerts and provides the dashboards analysts investigate from.
6. What is the difference between SIEM and SOAR?
SIEM detects: it correlates log data to surface alerts. SOAR responds: it automates enrichment, ticketing and containment after an alert exists. Most platforms now ship both.
7. What does a SOC Analyst do?
A SOC analyst monitors security alerts, triages false positives from real threats, investigates suspicious activity across logs, escalates confirmed incidents and supports containment.
8. What skills are required to become a SOC Analyst?
Networking fundamentals, Windows and Linux logging, SIEM query skills, log analysis, MITRE ATT&CK familiarity, incident response knowledge and threat intelligence basics.
9. Is SOC Analyst Training in Hyderabad suitable for beginners?
Yes, provided the programme starts with fundamentals — networking, operating systems and security concepts — before moving to SIEM work. Prioritise hands-on lab time over syllabus length.
10. What is the career path of a SOC Analyst?
Most start as an L1 analyst, move to L2 after roughly two to three years, then specialise — L3 analysis, threat hunting, incident response, detection engineering, or security architecture.