SOC 1 vs SOC 2 vs SOC 3: Key Differences Explained
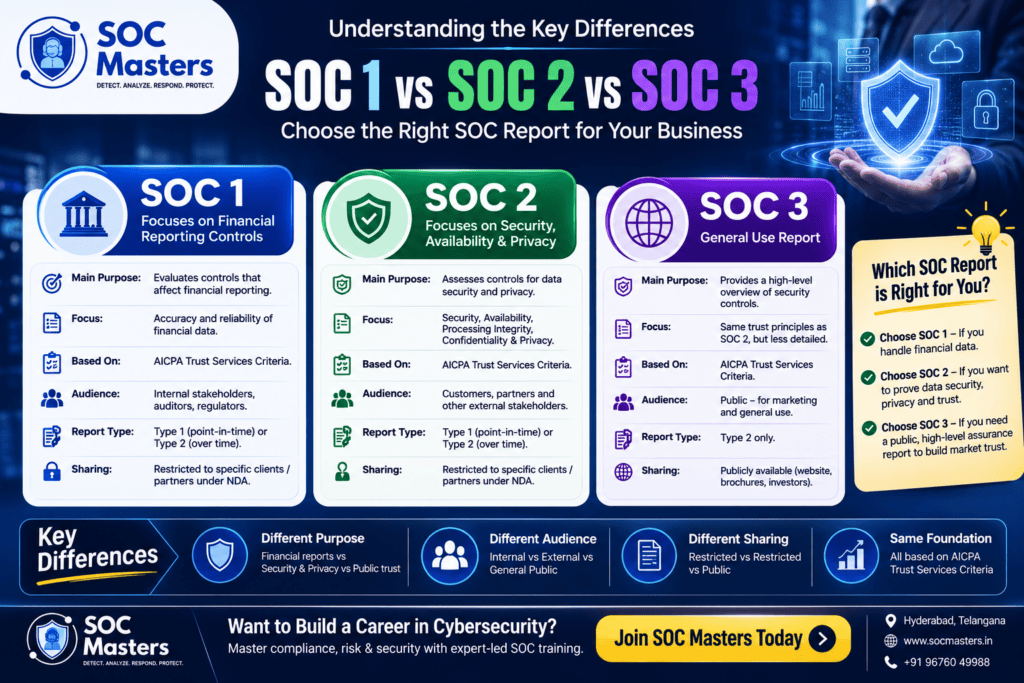
SOC 1, SOC 2, and SOC 3 are AICPA reporting standards for service organizations. SOC 1 covers internal controls over financial reporting. SOC 2 evaluates controls against the Trust Services Criteria — security, availability, processing integrity, confidentiality, and privacy. SOC 3 reports on the same criteria as SOC 2 but is a short, general-use summary a company can publish publicly on its website.
Table of Contents
Introduction
A vendor announces it is “SOC 2 compliant.” A finance team asks a payroll provider for its “SOC 1 report.” Meanwhile a security analyst is pulling six months of log retention evidence for an auditor. Three different conversations, one confusing acronym.
SOC reports are independent attestation reports produced by licensed CPA firms under standards set by the AICPA (American Institute of Certified Public Accountants). When Company A outsources operations to Company B, Company A still carries the risk. A SOC report gives Company A independent evidence that Company B’s internal controls are designed properly — and sometimes, that they worked over a period of time.
This matters to cybersecurity professionals for a reason often missed. A SOC report does not test your firewall. It tests whether the process around your firewall exists, is documented, is followed, and can be evidenced. That is a different discipline from threat detection, and it catches analysts out during their first audit cycle.
There is also a naming collision. “SOC” in SOC 2 means System and Organization Controls — a reporting framework. “SOC” in SOC Analyst means Security Operations Center — a team that monitors, detects, and responds to threats. Confusing them in an interview costs credibility.
Hyderabad has become one of India’s larger hubs for security operations delivery, with global capability centres, managed security providers, and product companies running monitoring teams from the city. Analysts who can work a SIEM console and explain how their monitoring supports a control requirement progress faster — much of why hands-on SOC Analyst Training in Hyderabad has become a common entry route.
What Is a SOC Report?
A SOC report — System and Organization Controls — is an independent examination of controls at a service organization: any company performing a function on behalf of another, such as a cloud host, payroll processor, data centre operator, SaaS platform, or managed security provider.
The framework is maintained by the AICPA, and the examination is performed by an independent CPA firm that issues an opinion. The company examined does not grade itself, and that independence is the point.
SOC reports exist because of a trust gap: a large enterprise cannot audit every vendor, and vendors cannot host a hundred customer audits a year. One examination serves many readers.
Core concepts:
- Internal controls — the policies, procedures, and technical measures used to achieve a stated objective.
- Attestation, not certification — a CPA firm expresses an opinion. Strictly, nobody “passes” SOC 2.
- Scope is chosen — the service organization defines which systems and criteria are in scope, so two SOC 2 reports are not automatically comparable.
- Point in time vs period of time — the Type I / Type II distinction, which changes what the report proves.
There are three main options: SOC 1, SOC 2, and SOC 3. The AICPA also publishes SOC for Cybersecurity and SOC for Supply Chain, outside this comparison.
What Is SOC 1?
A SOC 1 report covers controls at a service organization relevant to a user entity’s internal control over financial reporting (ICFR).
Plainly: if your service could cause an error in your customer’s financial statements, your customer’s auditor needs assurance about your controls.
SOC 1 engagements run under SSAE 18, specifically AT-C Section 320, which replaced SSAE 16 for reports dated on or after 1 May 2017.
Who uses it: service organizations such as payroll providers, transaction processors, and fund administrators; the user entity whose financials are affected; and the user auditor signing off those statements — the real audience.
SOC 1 Type I | SOC 1 Type II | |
What it tests | Whether controls are suitably designed | Design and operating effectiveness |
Timeframe | A single date | A period, commonly 6–12 months |
Evidence | Description and design review | Sampled testing across the period |
Typical use | First-year report, readiness signal | Ongoing annual assurance |
Type II carries far more weight — a control on paper and a control that ran reliably for a year are different things.
Example. A payroll company calculates salaries and statutory deductions for 400 clients. If its logic is wrong, or an unauthorised person can change pay rates, all 400 have a misstatement problem. Change management, access to the calculation engine, and output reconciliation are what SOC 1 examines. Note what is not the focus: SOC 1 is not a general security report.
What Is SOC 2?
A SOC 2 report examines controls against the Trust Services Criteria — what most people mean by “security compliance.”
SOC 2 engagements run under AICPA attestation standards (AT-C Sections 105 and 205). The criteria are defined in TSP Section 100, the 2017 Trust Services Criteria with Revised Points of Focus – 2022, which remains current. The 2022 update revised the supporting points of focus — explanatory guidance — but not the criteria themselves, which have been stable since 2017.
The five Trust Services Criteria:
- Security — protection against unauthorised access, disclosure, and damage. Also called the Common Criteria (CC1–CC9), covering control environment, risk assessment, logical and physical access, system operations, change management, and risk mitigation. Security is the only criterion required in every SOC 2 examination.
- Availability — the system is available as committed: uptime, capacity planning, backup, disaster recovery.
- Processing Integrity — processing is complete, valid, accurate, timely, and authorised.
- Confidentiality — confidential information is protected through encryption, classification, retention, and secure disposal.
- Privacy — personal information is handled in line with the organisation’s commitments. Distinct from confidentiality: privacy is specifically about personal data.
The other four are optional, selected based on customer commitments and buyer demands — which is why “we have SOC 2” is an incomplete statement.
How SOC 2 differs from SOC 1: SOC 1 protects the accuracy of financial reporting, against objectives the service organization sets around ICFR, and is read by financial auditors. SOC 2 protects data and systems against criteria the AICPA defines, and is read by security, procurement, and risk teams.
Type I / Type II applies identically. A SOC 2 Type II covers design and operating effectiveness over a period, typically 3 to 12 months. Most enterprise buyers now require Type II.
Review the criteria directly in the AICPA’s published document: <a href=”https://www.aicpa-cima.com/resources/download/2017-trust-services-criteria-with-revised-points-of-focus-2022″ target=”_blank” rel=”noopener”>2017 Trust Services Criteria (With Revised Points of Focus – 2022)</a>.
What Is SOC 3?
A SOC 3 report covers the same Trust Services Criteria as SOC 2, but is written for general use. The difference is not subject matter — it is detail and audience.
A SOC 2 report is restricted-use: it contains a detailed system description, the specific controls, the auditor’s tests, and the results including exceptions. That detail is sensitive, so SOC 2 reports are normally shared under NDA.
A SOC 3 report strips that out, keeping the auditor’s opinion, management’s assertion, and a short system description — but no control listing or test results. Revealing nothing sensitive, it can be published openly.
Key points:
- SOC 3 is derived from a SOC 2 examination. Organisations do not typically pursue it alone — they run SOC 2 and issue SOC 3 alongside.
- SOC 3 is general-use, with no separate Type I / Type II distinction in common practice.
- SOC 3 is a trust-signalling instrument. It answers “can we trust this vendor?” at a glance, not “what exactly did the auditor test?”
Who uses it: large cloud and SaaS providers with wide public customer bases, where publishing a short summary beats processing thousands of NDA requests.
SOC 1 vs SOC 2 vs SOC 3: Key Differences
Feature | SOC 1 | SOC 2 | SOC 3 |
Primary Focus | Internal control over financial reporting (ICFR) | Trust Services Criteria: security, availability, processing integrity, confidentiality, privacy | Same criteria as SOC 2, summarised |
Intended Audience | Customer’s finance team and their financial auditors | Customer’s security, risk, procurement, and compliance teams | General public — prospects, website visitors |
Reporting Purpose | Assurance the service does not distort financial statements | Detailed assurance on how data and systems are protected | Short, shareable trust signal |
Security Controls | Only where they affect financial reporting | Core subject of the report | Covered, without detailed control listings |
Public Availability | Restricted use, shared under NDA | Restricted use, shared under NDA | Freely publishable |
Type I | Yes — design at a point in time | Yes — design at a point in time | Not applicable in common practice |
Type II | Yes — design and operating effectiveness | Yes — design and operating effectiveness | Not applicable in common practice |
Typical Use | Payroll, transaction processing, fund administration | SaaS platforms, cloud providers, data processors | Public trust pages for large providers |
SOC 1 vs SOC 2 vs SOC 3: Which One Should a Company Choose?
None of these is universally better. They answer different questions.
Business model. If the service touches money movement or anything feeding a customer’s ledger, SOC 1 is likely relevant. If it holds or processes customer data, SOC 2 is the common expectation.
Customer requirements. In practice this decides it. Most organisations pursue a SOC report because a prospect asked during procurement, and the request usually names the report.
Regulatory expectations. Sector rules may push one way. SOC reports are not legal requirements — they are voluntary attestations that became a commercial norm.
Type of controls. Financial reporting controls point to SOC 1; information security and privacy controls point to SOC 2.
Public visibility. If a company wants something publishable without NDA friction, SOC 3 is added on top of SOC 2 — not instead of it.
Many organisations need more than one: a payroll SaaS platform can need SOC 1 (calculations affect client financials) and SOC 2 (it holds employee data).
This article is educational. Decisions about which SOC report to pursue should be made with a qualified CPA firm and your legal and compliance advisors.
SOC 1 vs SOC 2 vs SOC 3 for Cybersecurity Professionals
This is where compliance and security operations meet. During a SOC 2 examination, auditors request evidence — much of it from the security team’s tooling.
- Security controls — analysts rarely design controls but often operate them. Alert monitoring, review cadence, and escalation thresholds are all controls.
- Evidence collection — SIEM dashboards, alert queues, ticket histories, log retention configurations, sign-offs. If it cannot be evidenced, an auditor treats it as not happening.
- Security monitoring — proof that monitoring ran continuously, not that a tool was licensed.
- Access controls — access reviews, privileged account listings, joiner-mover-leaver records, MFA enforcement.
- Incident management — documented incidents with timestamps, severity, escalation path, and closure notes. Auditors read incident tickets closely.
- Vulnerability management — scan cadence, remediation against stated SLAs, exception handling.
- Log monitoring — retention periods, coverage of in-scope systems, and evidence logs were reviewed.
The theme: the audit tests the process, not the tool. A team with a modest SIEM and disciplined documentation fares better than one with an expensive platform and no records.
What Does a SOC Analyst Do?
A Security Operations Center analyst watches for, investigates, and responds to security events — a different job from the compliance work above, though the two intersect.
- Security monitoring — dashboards and alert queues across endpoint, network, identity, and cloud.
- Alert triage — separating true positives from noise. The largest part of an L1 analyst’s day.
- SIEM monitoring — working inside platforms like Microsoft Sentinel or Splunk, running queries and tuning rules.
- Log analysis — correlating events across sources to reconstruct what happened.
- Threat detection — recognising malicious patterns rather than noise.
- Incident escalation — handing off to L2 or L3 with a clear, complete summary.
- Incident response support — containment, evidence preservation, assisting the response lead.
- Documentation and reporting — case notes, shift handovers, metrics.
A realistic L1 shift: an impossible-travel alert fires — a user authenticating from Hyderabad and, forty minutes later, from another country. The analyst checks whether a VPN explains it, reviews sign-in history, confirms MFA, checks for mailbox rule changes, then closes it or escalates. That one investigation touches identity logs, SIEM queries, and documentation — and the ticket may later be sampled as audit evidence.
Building that judgement takes repetition on real tooling, which is why a good SOC analyst programme in Hyderabad is built around hands-on labs. See also SOC analyst roles and responsibilities and the SOC incident response process.
Why SOC Analysts Should Understand Compliance
To be direct: a SOC analyst is not an auditor, and understanding SOC 2 will not make anyone a better threat hunter. But the disciplines link in ways that affect a career.
Every monitoring activity maps to a control objective — knowing which one tells you why the work matters. Compliance frameworks are structured risk management, so understanding the risk a control addresses improves alert tuning; you stop suppressing the alert that is the only evidence for a control.
Analysts are also asked for evidence at short notice. One who can produce a clean log retention configuration or a documented incident timeline saves the compliance team days of work.
The practical takeaway: you do not need to run an audit. You need to explain what your monitoring proves and produce evidence when asked. That combination separates analysts who stay at L1 from those who move up.
SOC Analyst Skills Required in 2026
Skill | Why it matters |
SIEM | The primary working environment. Query fluency matters more than tool brand. |
Log Analysis | Reading Windows Event Logs, firewall, proxy, and cloud audit logs. |
Networking Fundamentals | TCP/IP, DNS, HTTP, ports, traffic flow. Without this, alerts are unreadable. |
Windows & Linux | Process behaviour, authentication, and native logging on both. |
Threat Detection | Distinguishing malicious patterns from operational noise. |
Incident Response | Containment, eradication, recovery, evidence handling. |
Vulnerability Management | Prioritising by real exposure, not raw CVSS. |
Threat Intelligence | Applying IOCs and TTPs, commonly mapped to MITRE ATT&CK. |
Security Monitoring | Sustained queue discipline and consistent triage quality. |
Basic Cloud Security | Identity, logging, and misconfiguration risk in cloud environments. |
Compliance Awareness | Understanding what your monitoring evidences. |
Soft skills matter too: handovers, escalation summaries, and incident write-ups are read under time pressure, so clear written English is a real differentiator.
SOC Tools Every Analyst Should Know
- Microsoft Sentinel — cloud-native SIEM and SOAR on Azure, queried with KQL. Widely deployed across Indian enterprises running Microsoft 365.
- Splunk — established log analytics and SIEM platform using SPL, common in large enterprises and financial services.
- IBM QRadar — SIEM with strong network flow analysis, widely used on-premises.
- CrowdStrike Falcon — endpoint detection and response with process-level telemetry.
- Microsoft Defender — endpoint, identity, email, and cloud app protection, integrating tightly with Sentinel.
- Wireshark — packet analysis for deep network investigation.
- Wazuh — open-source security monitoring with host intrusion detection; excellent for home labs because it costs nothing to run.
Learn one SIEM properly rather than three superficially — query logic transfers between platforms, menu navigation does not. See SIEM tools used by SOC analysts and technologies and tools used in a SOC.
SOC Analyst Training in Hyderabad: What Should You Learn?
Judge a job-oriented programme on how much time you spend inside real tools. The curriculum should cover:
- Cybersecurity fundamentals — CIA triad, threat landscape, attack lifecycle.
- Networking and operating systems — the base layer everything depends on.
- SOC operations — tiering model, shift structure, escalation matrix, SLAs.
- SIEM implementation — log source onboarding, parsing, correlation rules, dashboards.
- Microsoft Sentinel — KQL queries, analytics rules, workbooks, automation playbooks.
- Splunk — SPL fundamentals and dashboard creation.
- Log analysis — Windows Event IDs, Linux auth logs, firewall and proxy logs.
- Alert triage — a structured, repeatable investigation methodology.
- Incident response — the full lifecycle, with documentation practice.
- Threat intelligence — IOC handling and MITRE ATT&CK mapping.
- Compliance awareness — how monitoring supports control requirements.
- Real-time projects and hands-on labs — attack simulation, detection, investigation, reporting.
- Interview preparation — scenario questions, resume structure, mock interviews.
When comparing any SOC Analyst Course in Hyderabad, ask three questions: How many hours are spent in a live SIEM? Do I build an investigation portfolio? Who is teaching, and have they worked in a production SOC?
On SOC Analyst Certification, be realistic — certifications support a resume, they do not replace demonstrated ability. Vendor-neutral options like CompTIA CySA+ and Security+ are widely recognised, and the <a href=”https://learn.microsoft.com/en-us/credentials/certifications/security-operations-analyst/” target=”_blank” rel=”noopener”>Microsoft SC-200 Security Operations Analyst certification</a> aligns closely with Sentinel-based work. Compare SOC analyst certifications and review a SOC analyst course syllabus first. Candidates from non-IT backgrounds often start with broader cyber security training in Hyderabad.
SOC Architecture and Threat Intelligence
Threat intelligence gives raw alerts meaning. Indicators of compromise — IP addresses, domains, URLs and file hashes — are matched against incoming telemetry so analysts know whether an artefact has appeared in known campaigns. Above indicators sits knowledge of threat actors and their tactics and techniques.
The <a href=”https://attack.mitre.org/matrices/enterprise/” target=”_blank” rel=”noopener”>MITRE ATT&CK Enterprise Matrix</a> is the common language for this: analysts map an alert to a technique, then ask what comes next in the attack chain. Two 2026 updates matter. Version 18 replaced the old Detections and Data Sources model with Detection Strategies and Analytics, and version 19 — released 28 April 2026 — split Defense Evasion into two tactics, Stealth and Defense Impairment. Enterprise ATT&CK now spans 15 tactics and 222 techniques; material still teaching 14 tactics is out of date.
SOC Analyst Career Opportunities in Hyderabad
Hyderabad’s security hiring is driven by global capability centres, IT services firms, managed security providers, and product companies, many running follow-the-sun monitoring across shifts.
- SOC Analyst L1 — front-line monitoring and triage. The standard entry point.
- SOC Analyst L2 — deeper investigation, cross-source correlation, use case tuning.
- SOC Analyst L3 — advanced investigation, threat hunting, detection engineering.
- Security Analyst — broader remit across monitoring, vulnerability management, assessment.
- Incident Response Analyst — containment, forensics, recovery.
- Threat Analyst — intelligence collection and adversary tracking.
- Security Operations Engineer — building and maintaining the SOC platform itself.
Progression from L1 to L2 comes down to consistency: accurate triage, clean documentation, growing independence. See SOC analyst jobs in Hyderabad and the SOC analyst career roadmap.
SOC Analyst Salary in Hyderabad
The figures below are approximate market estimates compiled from publicly reported ranges. Actual compensation varies by employer type, shift pattern, certifications, and negotiation. These are not guarantees, and no training programme can promise a specific salary or placement.
Experience | Role | Approximate Annual Range (INR) |
0–2 Years | SOC Analyst L1 | ₹3.0 – ₹5.5 LPA |
2–4 Years | SOC Analyst L2 | ₹5.5 – ₹9.0 LPA |
4–7 Years | SOC Analyst L3 | ₹9.0 – ₹16.0 LPA |
7+ Years | Security Specialist / SOC Lead | ₹16.0 – ₹28.0 LPA |
What moves these numbers: employer type (product companies and global capability centres generally pay above IT services averages), shift allowances for 24×7 rotations, specialisation in detection engineering or cloud security, and demonstrable skill. For national comparison, see SOC analyst salary trends in India.
SOC 1 vs SOC 2 vs SOC 3: Real-World Examples
SaaS company (project management platform). Holds customer project data. No effect on financial statements. → SOC 2, likely Security and Confidentiality, plus Availability if uptime is contractually committed.
Cloud service provider. Runs infrastructure for thousands of customers who will ask for assurance. → SOC 2 Type II for enterprise diligence, plus SOC 3 published openly to reduce NDA overhead.
Payroll platform. Calculates salaries and statutory contributions flowing into client accounting records, and holds employee personal data. → SOC 1 for the financial dimension and SOC 2 for data protection.
Financial technology company. Processes transactions affecting merchant records. → SOC 1 for transaction processing controls, SOC 2 for account data security. Payment card security is separately governed by PCI DSS, a different framework.
Data processing service. Handles large volumes of client data where accuracy is the product. → SOC 2, with Processing Integrity a strong candidate alongside Security and Confidentiality.
These illustrate common patterns only. They are not legal, audit, or compliance advice; scoping decisions should involve qualified professionals.
SOC Compliance vs SOC Analyst: What's the Difference?
The most useful distinction in this article: the two SOCs are different terms sharing an acronym.
Area | SOC Compliance (System and Organization Controls) | SOC Analyst (Security Operations Center) |
Primary Focus | Independent attestation on internal controls | Real-time detection and response to threats |
Security Monitoring | Verifies monitoring exists and operated as described | Performs the monitoring |
Auditing | Central — the work product is an auditor’s opinion | Not an audit role; supplies evidence to auditors |
Incident Response | Checks a documented process exists and was followed | Executes the response |
Evidence | Requests, samples, and tests evidence | Generates evidence through daily operations |
SIEM | Reviews SIEM configuration and output as control evidence | Works inside the SIEM every shift |
Career Path | GRC analyst → compliance manager → internal audit | SOC L1 → L2 → L3 → threat hunter / detection engineer / SOC manager |
Both are legitimate careers requiring different aptitudes: compliance rewards structured documentation and stakeholder management, security operations rewards technical curiosity and fast pattern recognition.
Key Takeaways
- SOC 1 reports on controls relevant to a customer’s internal control over financial reporting, under SSAE 18 (AT-C 320), and is read primarily by financial auditors.
- SOC 2 reports on controls against the AICPA Trust Services Criteria, where Security is mandatory and the other four criteria are optional additions.
- SOC 3 covers the same criteria as SOC 2 but omits detailed test results, making it the only one of the three publishable publicly.
- Cybersecurity professionals interact with these reports through evidence — log retention, access reviews, alert histories, incident documentation — which is why compliance awareness makes analysts more valuable.
- “SOC” means two different things: System and Organization Controls and Security Operations Center. Distinguishing them is a mark of professional literacy.
Conclusion
SOC 1, SOC 2, and SOC 3 are not competing standards ranked worst to best. SOC 1 answers a financial reporting question, SOC 2 a data and systems security question, and SOC 3 makes the SOC 2 answer publishable. The choice depends on what a business does and what its customers ask for.
For security professionals, the value here is not audit expertise — it is context. When you know your log retention configuration, triage records, and incident tickets are the raw material of an assurance opinion, that work stops feeling like paperwork.
But compliance knowledge without operational skill is not a career. The analysts who progress can investigate a real alert, explain their reasoning, and document it clearly — abilities that come from repetition on live tooling.
Hyderabad continues to expand as a centre for security operations delivery, and demand for capable analysts remains steady. If you are considering SOC Analyst Training in Hyderabad, prioritise programmes built around hands-on labs, real investigation scenarios, and a portfolio you can defend in an interview. Build the practical skills first — the frameworks make far more sense once you have seen what they measure.
Ready to start? Explore hands-on SOC analyst training programmes and course details for curriculum, batch schedules, and lab structure.
Frequently Asked Questions
1. What is the difference between SOC 1 and SOC 2?
SOC 1 covers controls relevant to a customer’s internal control over financial reporting. SOC 2 covers controls against the Trust Services Criteria — security, availability, processing integrity, confidentiality, privacy. SOC 1 is read by financial auditors; SOC 2 by security and risk teams.
2. Is SOC 2 better than SOC 1?
No — they serve different purposes. SOC 1 applies when a service affects a customer’s financial reporting; SOC 2 when it handles customer data and systems. Some organisations need both.
3. What is SOC 3 used for?
SOC 3 is a short, general-use summary of a SOC 2 examination, used as a public trust signal on a website or trust page because it can be shared freely without an NDA.
4. Is SOC 3 publicly available?
Yes. A SOC 3 report is designed for general use and can be distributed openly. SOC 1 and SOC 2 reports are restricted-use documents normally shared under NDA.
5. What is the difference between SOC 2 Type I and Type II?
Type I assesses whether controls are suitably designed at a single point in time. Type II assesses design and operating effectiveness over a period, commonly 3 to 12 months. Type II provides stronger assurance and is what most enterprise buyers request.
6. Do SOC analysts need to understand SOC compliance?
Not in depth, but basic awareness helps. Analysts are regularly asked for audit evidence such as log retention settings, alert histories, and incident documentation.
7. What skills are required for a SOC analyst?
SIEM operation, log analysis, networking fundamentals, Windows and Linux administration, threat detection, incident response, vulnerability management, threat intelligence, basic cloud security, and clear written documentation.
8. Is SOC Analyst Training in Hyderabad good for beginners?
It can be, provided the programme is genuinely hands-on. Look for substantial live SIEM lab time, real investigation scenarios, and a portfolio of documented work rather than theory-only delivery.
9. What tools are used by SOC analysts?
Commonly Microsoft Sentinel, Splunk, and IBM QRadar for SIEM; CrowdStrike Falcon and Microsoft Defender for endpoint detection; Wireshark for packet analysis; and Wazuh as an open-source option.
10. What is the career path of a SOC analyst? T
ypically SOC Analyst L1 → L2 → L3, then specialisations such as threat hunting, detection engineering, or SOC management. Some move laterally into GRC, cloud security, or penetration testing.